Your people data.
Protected without compromise.
Your people data is the most sensitive thing you hold. So we publish the contract, the safeguards and every company we let near it. Read them before you talk to us.
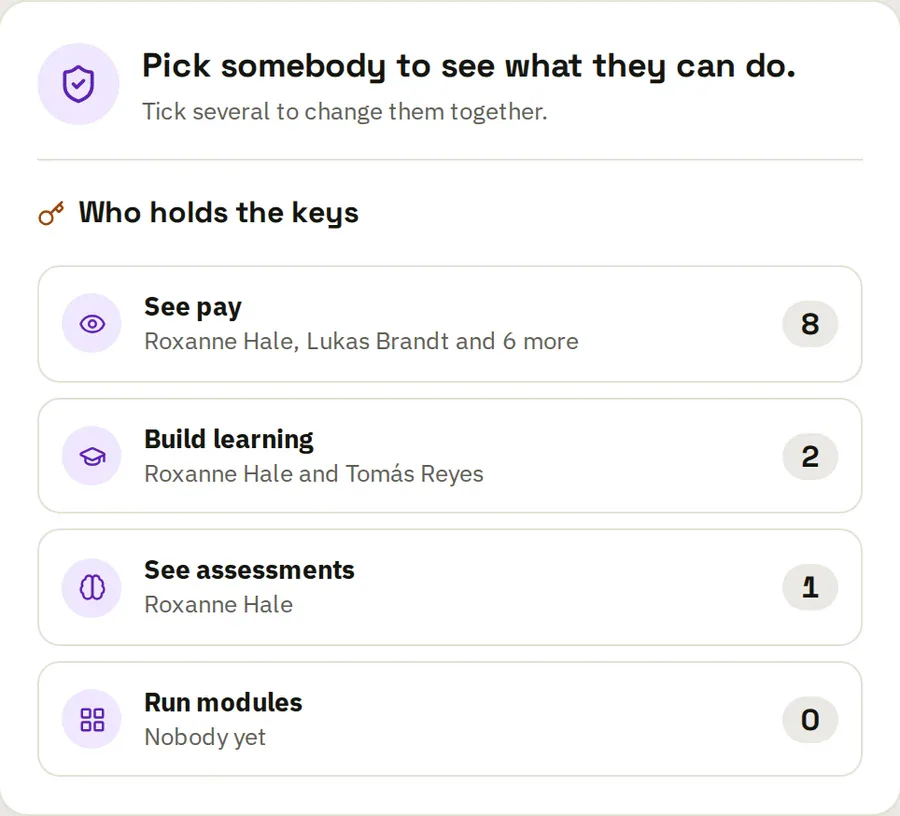
Permissions
Everyone sees what their job needs. Nothing more.
Pay, bank details and ID numbers are locked by default, even for admins.

See Sofia’s record as…
Admin is not enough. Pay has its own key.

- Job title
- Finance Manager
- Manager
- Hannah Osei
- Goals
- 3 of 4 on track
- Salary
- Withheld
- Bank account
- Withheld
- ID number
- Withheld
 Ask the assistant as Lukas and it sees this same view.
- Pay has its own keyEven admins need it to see salaries.
- Managers see their teamTheir own people. Not everyone.
- The assistant sees what you seeIt asks as you, so it opens nothing more.
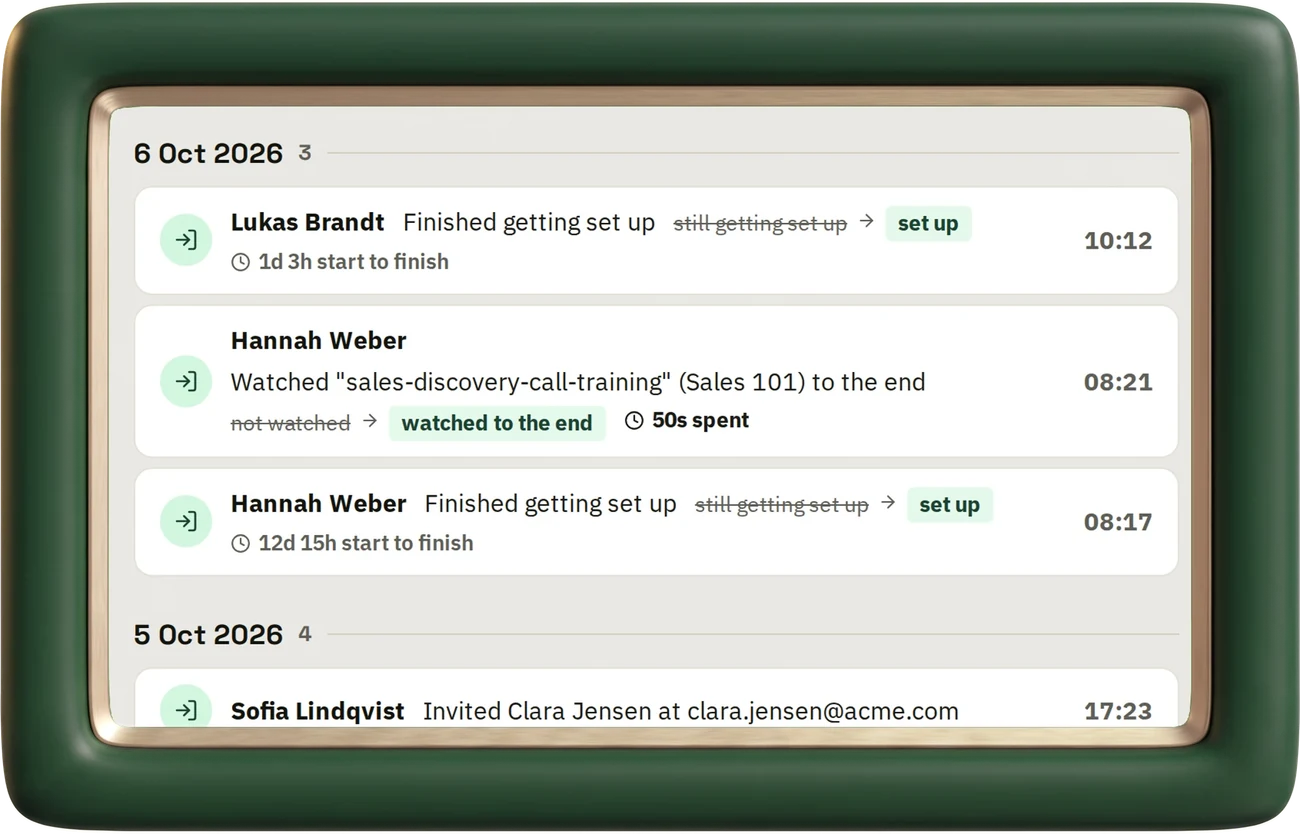
- Changes are recordedEvery change to a record keeps who made it and when.
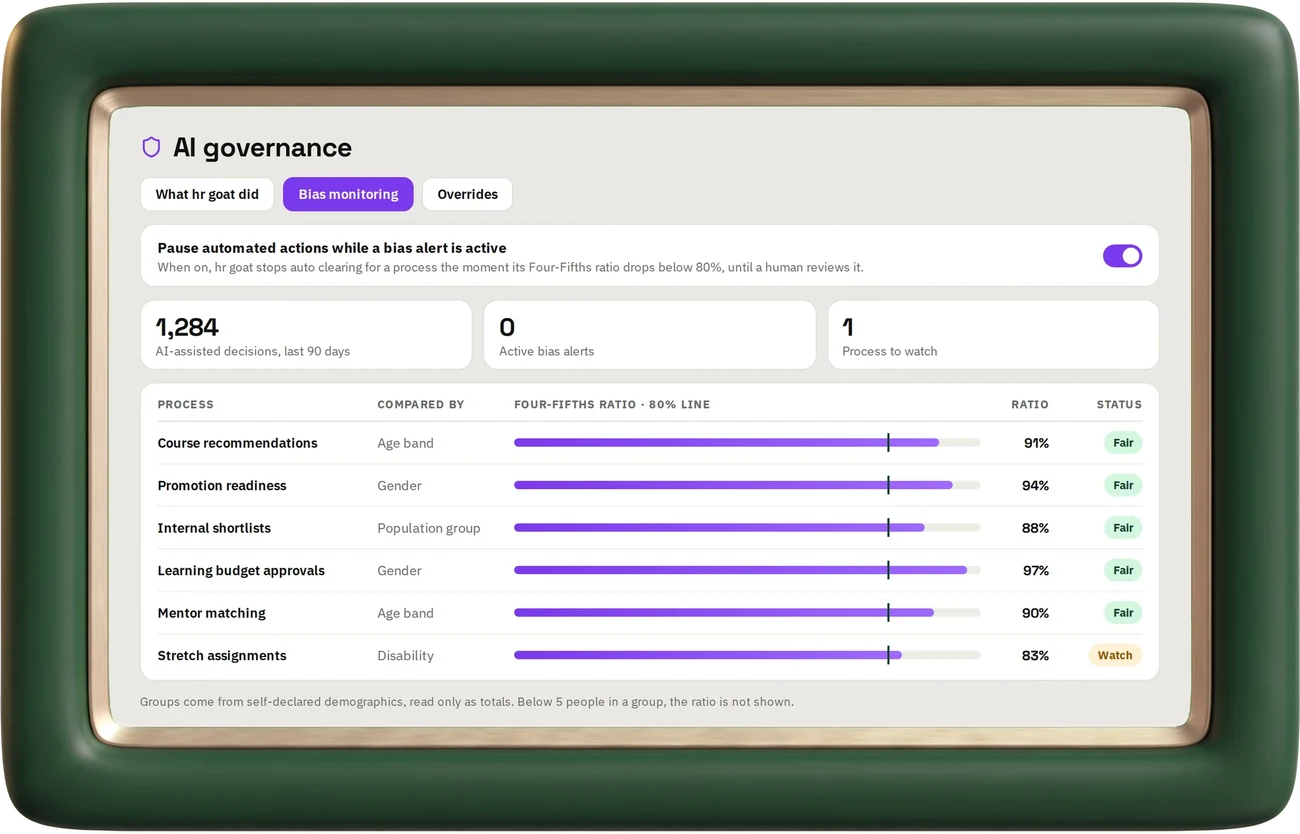
Your data does not go off and teach somebody else’s AI.
Business AI Africa certifies suppliers who can actually show where AI data goes and what it does there. We are a certified AI supplier.
In plain words: your data sits in one region we can name, it never trains anyone’s model, and every answer traces back to the row it came from. Change something and there is a log with your name on it.
Learn about Business AI AfricaCertified AI Supplier
Business AI Africa
Run to the international standard for information security.
Every control below is written down, tested and reviewed on a set cycle. Ask and we will walk you through any of them.
How we protect your data
Security by design. Not by default.
Engineering decisions baked into the platform from day one, not policies written for auditors.
Encryption everywhere
TLS 1.2 or above in transit, and inside our own network too. AES-256 at rest, with keys held and rotated in Google Cloud Key Management Service. Passwords are hashed one way and cannot be read back.
One region, and we can name it
Google Cloud europe-west1, St Ghislain, Belgium, inside the EEA. The same region for every customer. We will not move production hosting out of the EEA without 30 days’ notice and your right to object.
Your data never trains AI models
The assistant runs on Google Vertex AI in that same region and project, so your data never leaves it to reach a model. No training, no fine-tuning, no improving anyone’s model. It is in the DPA at Schedule 2, clause 14.2, not just here.
Least privilege, and a log of who looked
Least-privilege roles and mandatory multi-factor for anyone near production. Rights reviewed quarterly and revoked within a day of somebody leaving. Admin access is logged and kept for 12 months. No shared accounts.
Independent penetration testing
At least once a year and after any material change, on top of automated scanning. Critical findings fixed within 7 days, high within 30, medium within 90. Summary reports go to customers under Schedule 2, clause 11.2.
Deleting means deleting
A delete is staged and then verified. Nothing you click is instantly irreversible. Backups roll over on a 35 day cycle, and an index of what you deleted is re-applied on any restore, so it cannot come back.
Data protection compliance
The standards that matter. And the discipline behind them.
Two we are compliant with and registered under. One we are aligned to. We are careful about which word goes where.
General Data Protection Regulation
Full compliance with EU Regulation 2016/679 and the UK GDPR, and we are registered with the UK Information Commissioner’s Office. Every processing activity has a documented lawful basis, data subject rights are honoured within statutory timeframes, and a DPA comes with every contract.
Protection of Personal Information Act
Registered with the Information Regulator of South Africa under registration number 2026-066673. Personal information from South Africa is hosted in Belgium and is therefore transferred outside the Republic. These transfers are made in accordance with section 72 of POPIA, on the basis that the recipient is subject to a binding agreement providing an adequate level of protection, being the Google Cloud Data Processing Addendum together with the European Union Standard Contractual Clauses and the United Kingdom International Data Transfer Addendum.
Information Security Management
Our security management system is built and operated in alignment with ISO/IEC 27001. Controls span the full Annex A framework and are reviewed annually.
Individual rights
Your employees have rights. We honour them.
Every right is fulfilled within statutory timeframes across all applicable jurisdictions.
Individuals can request a copy of the personal data we hold about them.
Incorrect or incomplete personal data can be corrected on request.
Individuals can request deletion of their personal data, subject to lawful retention requirements.
Personal data is provided in a structured, machine-readable format on request.
Processing can be restricted while a dispute is being resolved.
Individuals can object to processing based on legitimate interests.
Common questions
Straight answers.
Most of it is already published.
The Data Processing Addendum, the technical and organisational measures behind it and the full sub-processor list are all on this site. No NDA, no form, no sales call. Read them before you talk to us.
Penetration test summaries, audit reports and security questionnaires: legal@hrgoat.ai.
Admin and controls
The admin console you would have built anyway. Already built.